Configure External IdP in GigaVUE‑FM
Prerequisites
You can use encryption and signing in IdP only when GigaVUE-FM uses an RSA-based certificate.
To configure external IdP (Active Directory Federation Services (ADFS)/Okta/Microsoft Azure) in GigaVUE‑FM:
- Select Authentication > Authentication Types.
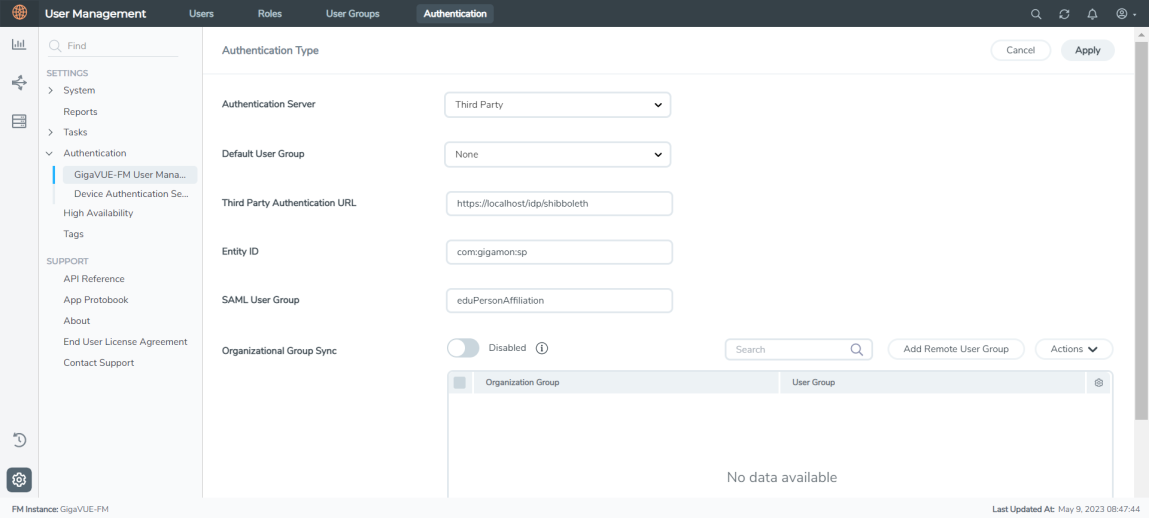
- Select Authentication Server as SAML 2.0.
- Enter the following details and click Apply.
|
Field |
Description |
|---|---|
|
IdP Metadata URL |
The IdP Metadata URL. Example: For ADFS: https://<<ADFS_HOSTNAME>>/FederationMetadata/2007-06/FederationMetadata.xml |
|
Entity ID |
Entity ID of the service provider (GigaVUE‑FM). Fetch the Service Provider metadata (which is GigaVUE‑FM’s metadata) from https://<FM IP Address>/saml/metadata. |
|
SAML User Group |
SAML User Group. This is used for authentication. The SAML User Group name entered here must match the SAML User Group configured in external IdP. |
|
Default User Group |
Default User Group |
|
Organizational Group Sync |
Map the GigaVUE‑FM group to the corresponding organizational groups in ADFS/OKTA/Microsoft Azure. |
Note: It is not required to enable Trust Store Node Certificate based authentication access.
You must restart the CMS process in GigaVUE-FM for the above configuration to be implemented. For an FMHA instance, restart the standby nodes first, followed by the active nodes.


